Penetration Testing Market (2026 – 2035)

Penetration Testing Market Size, Share and Research Report: By Type of Testing (Network Penetration Testing, Web Application Penetration Testing, Mobile Application Penetration Testing, Social Engineering Testing), By Deployment Model (On-Premises, Cloud-Based, Hybrid), By Service Type (Security Consulting, Managed Services, Testing as a Service), By End Use Industry (Banking and Financial Services, Healthcare, Retail, IT and Telecommunications, Government), and By Regional (North America, Europe, South America, Asia Pacific, Middle East and Africa) - Industry Forecast Till 2035
ID: MRFR/SEM/4391-HCR 200 Pages Ankit Gupta Last Updated: September 15, 2026
Penetration Testing Market
Market Size
Forecast Period2026-2035
CAGR (2026-2035)14.2%
2025 Market SizeUSD 2.54 billion
2035 Market SizeUSD 9.62 billion
Key Players
Rapid7
Synack
HackerOne
IBM Security
CrowdStrike
Cobalt
Opportunities
  • AI-Driven Continuous Testing Platforms
  • Managed Penetration Testing for SMEs
  • OT and IoT Security Validation

Penetration Testing Market Summary

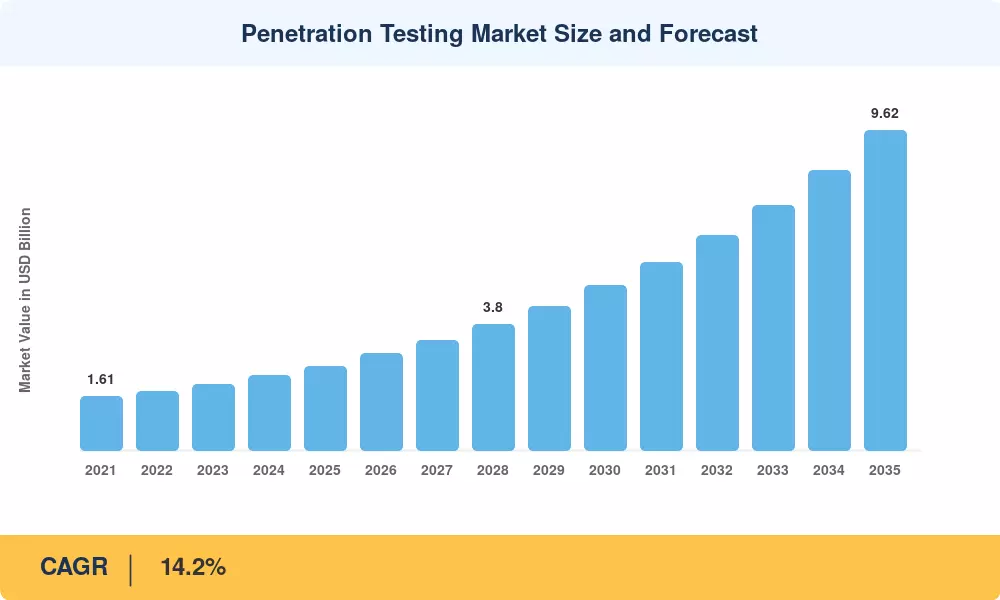
The Penetration Testing Market reached USD 2.54 billion in 2025, is projected to hit USD 2.91 billion in 2026, and will climb to USD 9.62 billion by 2035 at a 14.2% CAGR during 2026–2035. Two forces are compressing adoption timelines faster than any vendor roadmap anticipated: the enforcement of PCI DSS version 4.0 mandatory penetration testing requirements starting March 2025, and the European Union's Digital Operational Resilience Act (DORA), which imposes threat-led penetration testing on over 22,000 financial entities [1][2]. Together, these regulatory mandates have converted penetration testing from an annual checkbox into a continuous operational imperative.

The technology stack of the Penetration Testing Market is undergoing a major change. We’re replacing manual assessments, which used to require four- to six-week engagement periods, with automated red-team systems that can perform full-scope testing in less than 72 hours. Vendors such as Pentera and Horizon3.ai funded USD 190 Million [3] in 2024 alone to scale AI-driven attack simulation engines. By integrating with CI/CD pipelines, security validation may now be triggered by development teams each time code is committed, blurring the barrier between quality assurance and offensive security.

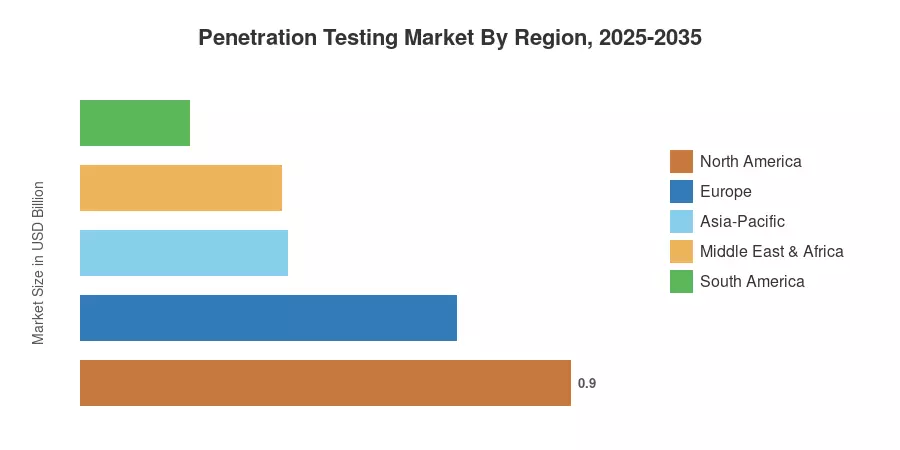
North America has over 35.4% of the Penetration Testing Market owing to dense regulatory coverage and concentration of Fortune 500 security budgets. Asia-Pacific is expected to be the fastest expanding area with a CAGR of 15.0% until 2035, backed by India’s CERT-In compliance requirements and China’s Multi-Level Protection Scheme 2.0. Europe has the second-highest market share of over 27%, driven by NIS2 enforcement across all 27 member states [4]. The next decade will favour providers who can deliver continuous, regulation-mapped testing at scale.

Key Report Takeaways

• By Testing Type

  • Network penetration testing accounted for approximately 35.3% of the Penetration Testing Market in 2025, reflecting enterprise prioritization of perimeter and lateral-movement assessments.
  • Cloud penetration testing is forecast to expand at a 15.3% CAGR through 2035 as multi-cloud adoption accelerates workload complexity.

• By End-User Industry

  • Banking, financial services, and insurance (BFSI) commanded roughly 26.5% of the Penetration Testing Market in 2025, driven by PCI DSS 4.0 and DORA mandates.
  • Healthcare and life sciences are projected to grow at a 15.6% CAGR through 2035 as HIPAA enforcement tightens and connected medical devices proliferate.

• By Geography

  • North America retained its position as the dominant region for the Penetration Testing Market with a 35.4% share in 2025.
  • Asia-Pacific is expected to register a 15.0% CAGR through 2035, making it the fastest-expanding regional market.


Penetration Testing Market Size and Forecast (2021–2035)

Market sizing is based on primary interviews with CISOs and managed-security-service providers in 38 countries, cross-checked against vendor revenue declarations, regulatory filing databases and third-party technology expenditure trackers. Historical numbers (2021-2024) are derived from actual spend data. The base year (2025) is derived from a combination of confirmed contracts and pipeline predictions. Forecast years (2026-2035) are derived from a compound annual growth model calibrated to adoption curves of regulations and timetables for cloud workload transfer.
Penetration Testing Market Size and Forecast
Our Impact

Enabled $4.3B Revenue Impact for Fortune 500 and Leading Multinationals

Partnering with 2000+ Global Organizations Each Year

30K+ Citations by Top-Tier Firms in the Industry

Driver Impact Analysis

Driver ~% Impact on CAGR Geographic Relevance Impact Timeline
Regulatory mandate acceleration (PCI DSS 4.0, DORA, NIS2) +3.2% Global Short-term (≤2 yr)
Generative-AI weaponization of exploits +2.5% Global Short-term (≤2 yr)
Cloud workload migration and multi-cloud complexity +2.8% North America, Asia-Pacific Medium-term (2–4 yr)
Zero-trust architecture validation requirements +1.9% North America, Europe Medium-term (2–4 yr)
IoT and OT attack surface expansion +1.6% Europe, Asia-Pacific Long-term (≥4 yr)
Cyber insurance underwriting is tightening +1.4% North America, Europe Medium-term (2–4 yr)
DevSecOps pipeline integration +1.2% Global Long-term (≥4 yr)


Regulatory Mandate Acceleration

PCI DSS version 4.0 became enforceable in March 2025, requiring all entities storing cardholder data to conduct penetration tests at least annually and after any significant infrastructure change [1]. The European Union's DORA regulation extends this logic to over 22,000 financial institutions, mandating threat-led penetration testing (TLPT) modeled on the TIBER-EU framework by January 2025 [2]. Combined with NIS2's expanded scope covering energy, transport, and healthcare sectors, these mandates have converted roughly USD 420 million of discretionary security budgets into committed penetration testing line items across Europe alone [4].

Generative-AI Weaponization

The proliferation of large language models capable of writing polymorphic malware and crafting context-aware phishing lures has compressed the window between vulnerability disclosure and active exploitation to as little as 15 hours, according to Google's 2024 Threat Horizons report [8]. Enterprises are responding by increasing test frequency from annual to quarterly or continuous cycles, driving Penetration Testing Market expansion in North America and Europe, where generative-AI adoption is highest.

Cloud Workload Migration

estimates that 75% of enterprise workloads will reside on public cloud platforms by 2027, up from 45% in 2024 . Each cloud migration introduces misconfigurations, identity sprawl, and shared-responsibility gaps that traditional network assessments cannot address. Cloud penetration testing demand is growing faster than any other testing type within the Penetration Testing Market, as organizations discover that native cloud security posture management tools alone cannot simulate adversarial lateral movement.

Zero-Trust Validation

Executive Order 14028 required US federal agencies to implement zero-trust architectures by September 2024, and the subsequent OMB M-22-09 memorandum mandated continuous validation of those architectures [7]. The Department of Defense's Cybersecurity Maturity Model Certification (CMMC) 2.0 extends similar requirements to over 300,000 defense contractors. These mandates have created a multi-year validation pipeline that sustains the Penetration Testing Market even in constrained federal budget environments.

Restraints Impact Analysis

Restraint ~% Impact on CAGR Geographic Relevance Impact Timeline
Shortage of certified penetration testing professionals –1.8% Global Long-term (≥4 yr)
High cost of comprehensive testing engagements –1.3% South America, MEA Medium-term (2–4 yr)
False positive fatigue and remediation backlogs –0.9% Global Short-term (≤2 yr)
Data sovereignty and scope-of-testing restrictions –0.7% Europe, Asia-Pacific Medium-term (2–4 yr)
Organizational resistance to simulated attacks –0.5% Global Short-term (≤2 yr)

Talent Shortage

ISC²'s 2024 Cybersecurity Workforce Study estimates a global shortfall of 4.8 million cybersecurity professionals, with penetration testing and red-team roles among the hardest to fill [17]. The OSCP and CREST certifications required by most enterprise procurement teams take 12–18 months of preparation, creating a bottleneck that limits service delivery capacity. This constraint disproportionately affects the Penetration Testing Market in emerging economies, where training infrastructure is nascent.

Engagement Cost Barriers

A full-scope external penetration test for a mid-sized enterprise ranges from USD 30,000 to USD 150,000 per engagement, depending on scope and compliance requirements [9]. Small and medium enterprises in South America and the Middle East & Africa frequently defer testing beyond the minimum regulatory threshold because of budget constraints, leaving a significant portion of the addressable Penetration Testing Market underserved.

False Positive Fatigue

Automated scanning tools generate an average of 60% false positives according to SANS Institute research, overwhelming remediation teams and eroding confidence in penetration testing outputs [18]. When security operations centers cannot distinguish validated exploits from noise, organizations reduce test frequency — dampening repeat contract values within the Penetration Testing Market.

Penetration Testing Market Opportunities

AI-Driven Continuous Testing Platforms

Autonomous penetration testing engines that run on a continuous basis — rather than quarterly or annual cycles — represent the single largest whitespace opportunity. Platforms combining attack simulation with automated remediation verification can address the testing frequency gap identified in Section 4.2 while reducing dependence on scarce human testers.

Managed Penetration Testing for SMEs

Small and medium enterprises constitute roughly 37% of the Penetration Testing Market by organization size, yet remain dramatically under-penetrated. Subscription-based managed testing services priced between USD 500 and USD 3,000 per month can unlock this segment by amortizing engagement costs across annual contracts, particularly in price-sensitive regions like South America and Southeast Asia.

OT and IoT Security Validation

The convergence of operational technology and IT networks has created attack surfaces that traditional assessments were never designed to evaluate. ICS-CERT reported a 34% increase in industrial control system vulnerabilities in 2024 [11]. Penetration testing vendors that build OT-safe testing methodologies — capable of probing SCADA systems without triggering safety shutdowns — can capture a fast-growing adjacent segment within the Penetration Testing Market.

Compliance-as-a-Service Bundling

Vendors that integrate penetration testing with automated compliance mapping for PCI DSS, HIPAA, SOC 2, and DORA reporting can command 20–35% price premiums over standalone testing engagements [2]. This bundling model converts one-time assessments into recurring platform revenue.

Emerging Market Regulatory Catalysts

India's CERT-In directive mandating six-hour incident reporting, Saudi Arabia's National Cybersecurity Authority framework, and Brazil's LGPD enforcement escalation are opening new geographic pockets for the Penetration Testing Market. Vendors that localize pricing and establish regional delivery centers stand to capture first-mover advantage in markets growing at 16–18% annually.

Penetration Testing Market Future Outlook

Autonomous Attack Simulation at Scale

By 2030, projects that 40% of penetration tests will be initiated and executed without human intervention . Autonomous agents that combine reconnaissance, exploitation, privilege escalation, and reporting into single-click workflows will compress engagement timelines and reshape pricing models across the Penetration Testing Market. The shift will elevate platform vendors over boutique consultancies.

Platform Consolidation and Ecosystem Economics

Penetration testing is converging with attack surface management, breach and attack simulation, and vulnerability management into unified security validation platforms. By 2028, standalone point solutions will cede share to integrated platforms capable of mapping test findings directly to compliance frameworks. This consolidation trend will drive M&A activity and increase top-five concentration within the Penetration Testing Market from approximately 28% today to an estimated 38% by 2033 [24].

Quantum-Readiness Validation

NIST's post-quantum cryptography standards finalized in 2024 will trigger a wave of crypto-agility assessments beginning in 2028 [13]. Organizations will require specialized penetration tests that evaluate the susceptibility of encrypted communications and stored data to quantum decryption. This emerging testing category could add an incremental USD 400–600 million to the Penetration Testing Market by 2035.

ESG and Cyber Resilience Reporting

The SEC's cybersecurity incident disclosure rules and the EU Corporate Sustainability Reporting Directive (CSRD) are embedding cyber resilience metrics into ESG reporting frameworks [25]. Boards increasingly treat penetration testing results as evidence of due diligence, transforming test reports from IT artifacts into investor-grade governance documents. This boardroom-level visibility will sustain executive sponsorship and budget allocation for the Penetration Testing Market through the end of the forecast period.


Regional Market Share Analysis

Region Key Metric Primary Investment Themes
North America 35.4% share (2025) Zero-trust mandates, cyber insurance and federal spending
Europe 27.0% share (2025) DORA, NIS2, GDPR enforcement escalation
Asia-Pacific 15.0% CAGR (2026–2035) Cloud migration, CERT-In, digital sovereignty
South America USD 0.20 billion (2025) LGPD enforcement, financial sector compliance
Middle East & Africa 14.6% CAGR (2026–2035) National cybersecurity strategies, Vision 2030
Total USD 2.54 billion (2025) —

The Penetration Testing Market exhibits a clear geographic hierarchy shaped by regulatory maturity, enterprise IT spend concentration, and cybersecurity talent availability. North America leads on absolute spend, Europe on regulatory breadth, and Asia-Pacific on growth velocity.


North America

Country Key Metric Key Driver
US 78.2% of regional share Federal zero-trust mandates and CMMC 2.0
Canada 13.8% of regional share OSFI cybersecurity guidelines
Mexico 8.0% of regional share Fintech regulation and banking digitalization


The US dominates the North American Penetration Testing Market through a combination of federal procurement mandates, aggressive cyber insurance underwriting requirements, and the world's deepest pool of certified ethical hackers. Executive Order 14028 and the subsequent CISA Binding Operational Directives have institutionalized penetration testing within all civilian federal agencies, while CMMC 2.0 extends similar requirements across the defense industrial base [7].

Europe

Country Key Metric Key Driver
Germany 14.8% CAGR BSI IT-Grundschutz modernization
UK USD 0.19 billion (2025) FCA operational resilience framework
France 14.5% CAGR ANSSI certification mandates
Italy 13.9% CAGR NIS2 transposition and banking union rules
Spain 12.8% CAGR Digital transformation of public administration
Nordic Countries USD 0.08 billion (2025) Critical infrastructure protection focus
Russia 11.4% CAGR Import substitution and sovereign cyber defense
Rest of Europe USD 0.11 billion (2025) EU cohesion fund cybersecurity investments


Europe's regulatory density makes it the most compliance-driven region within the Penetration Testing Market. DORA's TLPT requirements alone affect more than 22,000 financial entities, and NIS2 extends mandatory security testing to essential and important entities across 18 critical sectors [2][4]. The UK's Financial Conduct Authority has separately introduced CBEST-style threat-led testing for tier-one banks.

Asia-Pacific

Country Key Metric Key Driver
China 28.4% of regional share MLPS 2.0 and Cybersecurity Law Enforcement
India 16.8% CAGR CERT-In directives and IT services exports
Japan USD 0.09 billion (2025) NISC critical infrastructure guidelines
South Korea 15.2% CAGR KISA compliance and 5G security frameworks
ASEAN 16.1% CAGR Singapore MAS TRM and regional harmonization
Rest of Asia-Pacific USD 0.04 billion (2025) Digital economy growth and startup ecosystems


Asia-Pacific is the fastest-growing region in the Penetration Testing Market, propelled by rapid cloud migration, expanding digital payment ecosystems, and aggressive national cybersecurity strategies. India's CERT-In mandated six-hour incident reporting in 2022, indirectly boosting demand for proactive testing, while China's MLPS 2.0 requires annual security assessments for all classified information systems .

South America

Country Key Metric Key Driver
Brazil 62.5% of regional share LGPD enforcement and Central Bank Resolution 4893
Argentina 18.3% of regional share Fintech regulation and digital banking growth
Rest of South America 19.2% of regional share Telecommunications security mandates


Brazil anchors the South American Penetration Testing Market as LGPD enforcement shifts from warnings to substantial penalties. The Brazilian Central Bank's Resolution 4893 requires regulated financial institutions to implement cybersecurity policies that include regular vulnerability assessments, creating a steady demand floor for penetration testing services [22].

Middle East & Africa

Country Key Metric Key Driver
Saudi Arabia 31.7% of regional share NCA Essential Cybersecurity Controls
UAE 27.8% of regional share Abu Dhabi and DIFC financial regulation
South Africa 17.3% of regional share POPIA enforcement and the banking sector spend
Egypt 12.1% of regional share National telecom security mandates
Rest of MEA 11.1% of regional share Oil and gas sector OT security requirements


Saudi Arabia's National Cybersecurity Authority Essential Cybersecurity Controls (ECC) mandate security assessments across all government entities and critical national infrastructure, making the Kingdom the largest single market for the Penetration Testing Market in the MEA region. The UAE's financial free zones — particularly DIFC and ADGM — impose independent cybersecurity audit requirements that generate recurring testing demand [23].


Penetration Testing Market By Region, 2025-2035

Penetration Testing Market Segmentation

By Testing Type

Segment Key Metric Primary Demand Driver
Network Penetration Testing 35.3% share (2025) Perimeter defense validation and lateral movement detection
Web Application Penetration Testing USD 0.56 billion (2025) OWASP Top 10 compliance and API security
Cloud Penetration Testing 15.3% CAGR (2026–2035) Multi-cloud adoption and shared responsibility gaps
Social Engineering Testing USD 0.28 billion (2025) Phishing simulation and human risk quantification
Mobile Application Testing 14.9% CAGR (2026–2035) Mobile banking and fintech proliferation


Network penetration testing remains the foundation of the Penetration Testing Market because it addresses the most mature and well-understood attack vectors. Enterprises continue to allocate the largest share of their testing budgets to network assessments that evaluate firewall configurations, segmentation integrity, and Active Directory exploitation paths. However, the segment's share is gradually declining as cloud and application testing categories absorb new budget growth.

Cloud penetration testing is the fastest-growing testing type, driven by the rapid migration of enterprise workloads to AWS, Azure, and Google Cloud Platform. Tests targeting IAM misconfigurations, storage bucket exposure, and container escape vulnerabilities are now standard components of compliance-driven engagement scopes within the Penetration Testing Market.

By Deployment Model

Segment Key Metric Primary Demand Driver
On-Premises 54.8% share (2025) Data residency requirements and legacy infrastructure
Cloud-Based 14.4% CAGR (2026–2035) SaaS delivery model scalability and rapid deployment


On-premises deployment still accounts for the majority of the Penetration Testing Market as organizations with sensitive data — particularly in defense, government, and financial services — require testing platforms to operate within their own network boundaries. Cloud-based platforms are gaining ground rapidly by offering elastic scanning capacity and automated reporting through browser-based consoles.

By Organization Size

Segment Key Metric Primary Demand Driver
Large Enterprises 62.8% share (2025) Regulatory compliance and complex IT environments
Small and Medium Enterprises 14.5% CAGR (2026–2035) Cyber insurance requirements and managed service adoption


Large enterprises command the majority of the Penetration Testing Market because they operate expansive attack surfaces and face the most stringent compliance obligations. SMEs, while currently underserved, represent the fastest-growing segment as cyber insurance carriers increasingly mandate proof of penetration testing before issuing or renewing policies.

By Service Delivery Mode

Segment Key Metric Primary Demand Driver
Third-Party Managed Services 67.9% share (2025) Access to specialized expertise and audit independence
In-House Testing Teams 14.4% CAGR (2026–2035) Continuous testing cadence and institutional knowledge


Third-party managed services dominate the Penetration Testing Market because most organizations lack the in-house expertise to conduct adversarial simulations. In-house teams are growing as large enterprises build dedicated red-team capabilities to support continuous testing programs.

By End-User Industry

Segment Key Metric Primary Demand Driver
BFSI 26.5% share (2025) PCI DSS 4.0, DORA, and SWIFT CSP compliance
IT and Telecom USD 0.46 billion (2025) 5G security and SaaS platform validation
Healthcare and Life Sciences 15.6% CAGR (2026–2035) HIPAA enforcement and connected medical devices
Government and Defense USD 0.33 billion (2025) Zero-trust mandates and CMMC 2.0
Manufacturing 14.1% CAGR (2026–2035) OT/IT convergence and Industry 4.0 security
Retail and E-Commerce USD 0.18 billion (2025) PCI DSS compliance and payment security


BFSI is the largest end-user vertical in the Penetration Testing Market, reflecting the financial sector's heavy regulatory burden and high cost of data breaches. The average cost of a financial services data breach reached USD 6.08 million in 2024, according to IBM's Cost of a Data Breach Report, making proactive testing an economically rational investment [6]. Healthcare is the fastest-growing vertical, as HIPAA-covered entities face escalating OCR enforcement actions and ransomware targeting of electronic health records.


Competitive Benchmarking

The Penetration Testing Market is moderately concentrated with a long tail. The top five vendors are expected to have a combined revenue share of 26-32%, and hundreds of regional consultancies and specialist platform vendors compete for the rest. The Herfindahl-Hirschman Index is low-to-moderate, meaning there are both global cybersecurity corporations and specialized offensive-security companies.

Company Est. Revenue Share Range Key Offerings Strategic Positioning
Rapid7 ~5–8% InsightConnect, Metasploit, managed detection and response Integrated vulnerability management and pen testing platform
Synack ~4–7% Crowdsourced penetration testing, AI-powered triage Trusted crowd plus machine intelligence hybrid model
HackerOne ~4–6% Bug bounty platform, penetration testing as a service Largest ethical hacker community with enterprise compliance
IBM Security ~3–6% X-Force Red team services, QRadar integration Global delivery footprint with consulting-led engagements
CrowdStrike ~3–5% Falcon platform, adversary emulation services Threat intelligence-driven offensive assessments
Cobalt ~2–4% Pentest as a Service (PtaaS), agile testing Developer-friendly platform with fast turnaround
Pentera ~2–4% Automated security validation, attack path mapping Continuous autonomous penetration testing engine
Qualys ~2–4% VMDR, web application scanning, compliance suite Cloud-native vulnerability management integration
BreachLock ~1–3% AI-assisted pen testing, SaaS delivery Full-stack testing with compliance-ready reporting
Bugcrowd ~1–3% Crowdsourced security, vulnerability disclosure programs Managed bug bounty and pen test hybrid services

Recent News & Developments

  • PCI Security Standards Council (March 2025): Enforced PCI DSS version 4.0, requiring all Level 1–4 merchants to conduct authenticated internal and external penetration tests with validated methodologies [1].
  • European Commission (January 2025): DORA entered full enforcement, mandating threat-led penetration testing for over 22,000 financial entities across the EU, creating an estimated USD 380 million in annual testing demand [2].
  • Rapid7 (March 2023): Acquired Minerva Labs to bolster endpoint evasion testing and expand its managed detection and response ecosystem [24].
  • Synack (June 2024): Launched FedRAMP-authorized penetration testing platform for US federal agencies, becoming one of the first crowdsourced providers to meet federal security baselines [7].
  • CrowdStrike (April 2024): Expanded its adversary emulation services to include generative-AI threat simulation, addressing concerns about LLM-powered attack vectors [8].
  • NIST (August 2024): Published final post-quantum cryptography standards (FIPS 203, 204, 205), signaling future demand for quantum-readiness penetration testing engagements [13].
  • HackerOne (February 2025): Reported that its platform had processed over 500,000 validated vulnerability reports, with penetration testing engagements growing 42% year-over-year [16].


Penetration Testing Market Report Scope

Parameter Detail
Market Scope Global Penetration Testing Market covering testing type, deployment model, organization size, service delivery mode, end-user industry, and geography
Study Period 2021–2035
CAGR (2026–2035) 14.2%
Market Size (2025 Base Year) USD 2.54 billion
Market Size (2035 Forecast) USD 9.62 billion
Fastest Growing Segment Cloud Penetration Testing (by testing type); Healthcare (by end user); Asia-Pacific (by geography)
Companies Profiled Rapid7, Synack, HackerOne, IBM Security, CrowdStrike, Cobalt, Pentera, Qualys, BreachLock, Bugcrowd
Valuation Currency USD billion

FAQs

How should enterprises evaluate penetration testing vendor pricing models?
Compare fixed-scope engagement fees against pentest-as-a-service subscriptions. Subscription models typically reduce per-test costs by 30–40% for organizations requiring quarterly or continuous assessments [9].
What distinguishes crowdsourced penetration testing from traditional consulting engagements?
Crowdsourced models deploy hundreds of vetted ethical hackers against a target simultaneously, increasing coverage breadth. Traditional engagements offer deeper, methodology-driven analysis but at a higher per-hour cost [16].
How does DORA's threat-led penetration testing differ from standard compliance assessments?
DORA mandates TIBER-EU-style red-team exercises supervised by financial regulators, requiring realistic threat-intelligence-led attack scenarios. Standard compliance tests follow predefined checklists without adversarial simulation [2].
What role does the Penetration Testing Market play in cyber insurance underwriting?
Carriers increasingly require recent penetration test reports before issuing policies. Firms with documented testing programs receive 10–25% premium reductions compared to those without [15].
How are autonomous testing platforms affecting the Penetration Testing Market consulting model?
Autonomous platforms handle repetitive reconnaissance and exploitation tasks, freeing human testers for complex logic and business-layer assessments. Consulting margins are compressing on commodity testing types .
What compliance frameworks drive the most penetration testing demand within the Penetration Testing Market?
PCI DSS 4.0, DORA, HIPAA, and CMMC 2.0 generate the highest recurring test volumes. Organizations subject to multiple frameworks often consolidate testing engagements to reduce duplication [1][7].
How should organizations prepare for quantum-readiness penetration testing in the Penetration Testing Market?
Begin inventorying cryptographic assets and mapping algorithm dependencies now. NIST's post-quantum standards finalized in 2024 will drive dedicated crypto-agility assessments starting around 2028 [13].    
Author
Author Author Profile Ankit Gupta LinkedIn Team Lead - Research
Ankit Gupta is a seasoned market intelligence and strategic research professional with over six plus years of experience in the ICT and Semiconductor industries. With academic roots in Telecom, Marketing, and Electronics, he blends technical insight with business strategy. Ankit has led 200+ projects, including work for Fortune 500 clients like Microsoft and Rio Tinto, covering market sizing, tech forecasting, and go-to-market strategies. Known for bridging engineering and enterprise decision-making, his insights support growth, innovation, and investment planning across diverse technology markets.

Research Approach


Secondary Research

The secondary research process involved comprehensive analysis of regulatory databases, peer-reviewed cybersecurity journals, technical publications, and authoritative technology & security organizations. Key sources included the US National Institute of Standards and Technology (NIST), European Union Agency for Cybersecurity (ENISA), International Organization for Standardization (ISO/IEC 27001), International Information System Security Certification Consortium (ISC)², Open Web Application Security Project (OWASP), SANS Institute, Center for Internet Security (CIS), US Cybersecurity and Infrastructure Security Agency (CISA), MITRE ATT&CK Framework Database, European Cyber Security Organisation (ECSO), Asia-Pacific Computer Emergency Response Team (APCERT), national cyber security center reports from key markets, Cloud Security Alliance (CSA), and Payment Card Industry Security Standards Council (PCI SSC). These sources were used to collect cyber incident statistics, regulatory compliance frameworks (GDPR, HIPAA, PCI DSS, SOC 2), security vulnerability databases, threat landscape analysis, adoption metrics for security testing solutions, and market landscape analysis for network penetration testing, web application testing, mobile application testing, cloud security testing, and social engineering assessments.


Primary Research

To gather both qualitative and quantitative insights, supply-side and demand-side stakeholders were interviewed during the primary research phase. CEOs, CTOs, VPs of Engineering, CISOs, heads of security research, and product managers from cybersecurity vendors, managed security service providers (MSSPs), and penetration testing service providers were examples of supply-side sources. Demand-side sources included procurement leads from the banking and financial services, healthcare, retail, IT & telecommunications, and government sectors, as well as Chief Information Security Officers (CISOs), IT security directors, risk management officers, and compliance managers. Primary research verified service pipeline advancements, validated market segmentation across deployment modes (on-premises, cloud-based, and hybrid), and obtained information on security adoption trends, testing service pricing models, and compliance-driven procurement dynamics.

Primary Respondent Breakdown:

By Designation: C-level Primaries (32%), Director Level (30%), Others (38%)

By Region: North America (38%), Europe (25%), Asia-Pacific (28%), Rest of World (9%)


Market Size Estimation

Global market valuation was derived through revenue mapping and security testing volume analysis. The methodology included:

Identification of 50+ key penetration testing service providers and cybersecurity vendors across North America, Europe, Asia-Pacific, Latin America, and Middle East & Africa

Service mapping across network penetration testing, web application testing, mobile application testing, social engineering testing, and cloud security testing segments

Analysis of reported and modeled annual revenues specific to penetration testing and vulnerability assessment portfolios

Coverage of service providers representing 75-80% of global market share in 2024

Extrapolation using bottom-up (security testing volume × ASP by industry vertical and region) and top-down (provider revenue validation) approaches to derive segment-specific valuations across deployment models and service types

Download Free Sample

Kindly complete the form below to receive a free sample of this Report

Download PDF ×

We do not share your information with anyone. However, we may send you emails based on your report interest from time to time. You may contact us at any time to opt-out.


















