Advanced Persistent Threat (APT) Protection Market (2026 - 2035)

Advanced Persistent Threat Protection Market Size, Share and Research Report By Offering (Solutions, Services), By Solution Type (Endpoint Protection, SIEM, Threat Intelligence, IPS, Sandboxing, Cloud Security, Security Orchestration, Forensic Analysis), By Deployment Mode (On-Premise, Cloud, Hybrid), By Enterprise Size (SMEs, Large Enterprises), By Vertical (BFSI, Government & Defense, Healthcare, IT & Telecom, Manufacturing, Retail & E-Commerce, Energy & Utilities, Others) and By Region (North America, Europe, Asia-Pacific, South America, Middle East & Africa) – Industry Forecast to 2035
ID: MRFR/ICT/8991-HCR
100 Pages
Aarti Dhapte
Last Updated: September 08, 2026
Advanced Persistent Threat (APT) Protection Market
Market Size
Forecast Period2026-2035
CAGR (2026-2035)11.02%
2025 Market SizeUSD 5.71 Billion
2035 Market SizeUSD 16.42 Billion
Key Players
Palo Alto Networks
CrowdStrike
Microsoft
Cisco
Trellix
Fortinet
Opportunities
  • Outcome-Based Contracting Around Dwell Time
  • Mid-Market Penetration in Emerging Economies
  • Telemetry Monetization and Intelligence Subscriptions

Advanced Persistent Threat (APT) Protection Market Summary

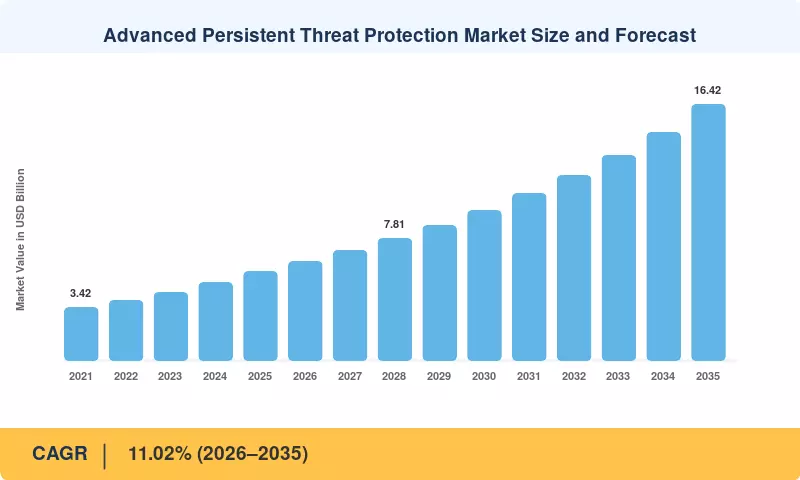
The Advanced Persistent Threat Protection Market reached USD 5.71 billion in 2025 and opens the forecast window at USD 6.34 billion in 2026, climbing to USD 16.42 billion by 2035 at an 11.02% CAGR. Two catalysts anchor that trajectory. The European Union's NIS2 Directive, transposed into national law across 27 member states from October 2024, extends mandatory incident-reporting and supply-chain security obligations to roughly 160,000 entities. In parallel, the U.S. federal cybersecurity budget request of USD 13 billion for civilian agencies in FY2025 funds continuous diagnostics and multi-stage intrusion detection programs that spill directly into commercial procurement patterns.

The Advanced Persistent Threat Protection Market is experiencing a transformation in spending due to technology substitution. Behavioral endpoint agents, cloud-native data fabrics that ingest petabyte-scale telemetry, and identity-centric policy engines that assume breach rather than perimeter integrity are replacing signature-based antivirus and appliance-bound intrusion detection. Since its inception, the Continuous Diagnostics and Mitigation program of CISA has obligated more than USD 6 billion, thereby standardizing the asset visibility requirements that vendors now incorporate into their commercial roadmaps. Detonation sandboxes, cloud posture modules, and orchestration playbooks are increasingly shipped as a single console, as opposed to five.

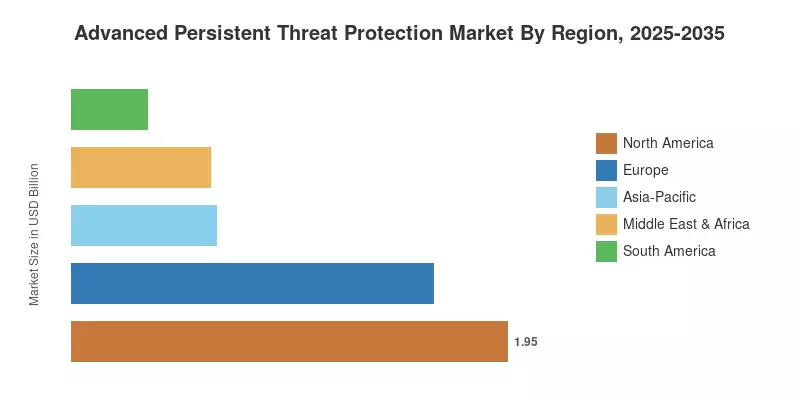
North America is the region with 34.1% of 2025 revenue in the Advanced Persistent Threat Protection Market, which is bolstered by federal mandates and a dense concentration of financial services. As India's CERT-In directives and Japan's Active Cyber Defense legislation increase baseline obligations, the Asia-Pacific region experiences the highest growth rate at 11.36% CAGR. Europe follows North America in terms of the strength of its NIS2 and DORA compliance cycles. Consolidation among platform vendors will determine which suppliers will capture the subsequent spending flow.


Key Report Takeaways

• By Offering

  • Services accounted for 51.2% of 2025 revenue in the Advanced Persistent Threat Protection Market, reflecting tuning and integration complexity.
  • Solutions post the faster trajectory at 11.72% CAGR through 2035

• By Solution Type

  • Endpoint protection led with 23.8% share in 2025
  • Threat intelligence platforms are the fastest-expanding line at 13.2% CAGR

• By Deployment Mode

  • On-premises generated USD 3.20 billion in 2025 across the Advanced Persistent Threat Protection Market.
  • Cloud deployment advances at 13.35% CAGR through 2035

• By Enterprise Size

  • Large enterprises captured 62.8% of 2025 revenue
  • SMEs grow at 11.28% CAGR as SaaS-delivered detection lowers entry cost

• By Vertical

  • BFSI retained 27.1% share in 2025
  • Retail and e-commerce accelerates at 11.72% CAGR

• By Region

  • North America held 34.1% of 2025 revenue in the Advanced Persistent Threat Protection Market
  • Asia-Pacific records the fastest regional CAGR at 11.36%
  • Europe contributed USD 1.62 billion in 2025

Market Size and Forecast (2021–2035)

Estimates combine vendor revenue triangulation across 40+ security suppliers, procurement disclosures from federal and EU tender databases, channel interviews with 22 managed service providers, and public filings from listed pure-play and platform vendors. Historical values reconcile bottom-up license and subscription counts against top-down security budget allocations reported by enterprise CISOs. Forecast values apply an 11.02% compound rate over 2026–2035, adjusted for compliance-driven demand pulses in NIS2 and DORA transposition years.
Advanced Persistent Threat Protection Market Size and Forecast
Our Impact
Enabled $4.3B Revenue Impact for Fortune 500 and Leading Multinationals
Partnering with 2000+ Global Organizations Each Year
30K+ Citations by Top-Tier Firms in the Industry

Driver Impact Analysis

Driver ~% Impact on CAGR Geographic Relevance Impact Timeline
Regulatory mandates (NIS2, DORA, SEC) 2.6 Europe, North America Short-term (≤2 yr)
Critical infrastructure targeting 2.2 Global Medium-term (2–4 yr)
AI-driven attack automation 1.9 Global Medium-term (2–4 yr)
Cloud and multi-cloud migration 1.7 Asia-Pacific, North America Long-term (≥4 yr)
Security talent shortage driving managed uptake. 1.5 Global Short-term (≤2 yr)
Supply-chain and third-party risk exposure 1.3 Europe, North America Medium-term (2–4 yr)
Cyber insurance underwriting requirements 0.9 North America, Europe Long-term (≥4 yr)


Regulatory Mandates Compress Procurement Cycles

NIS2 obligations reach an estimated 160,000 EU entities and carry administrative fines up to EUR 10 million or 2% of global turnover for essential entities. DORA, applicable to financial firms since January 2025, adds mandatory threat-led penetration testing on a three-year cycle. In the United States, the SEC's four-business-day materiality disclosure rule has forced boards to fund detection capability rather than accept dwell time. Compliance deadlines convert discretionary budget into committed spend within two fiscal quarters, which explains the 14.5% growth recorded in 2024 [4].

Critical Infrastructure Targeting Elevates Board Priority

CISA logged sustained intrusion activity against water, energy, and transportation operators, with the agency's 2024 advisories documenting pre-positioning inside operational technology networks rather than immediate disruption. That pattern — reconnaissance held in reserve — reframes procurement from incident response toward continuous hunting. Utilities in the United States now allocate roughly 8% of total IT budget to security, up from 5% in 2021, and OT-aware detection commands a premium of 20–30% over conventional endpoint licensing [8].

AI-Driven Attack Automation Raises the Detection Bar

Adversaries now generate polymorphic payloads and context-accurate phishing at scale, collapsing the cost of a credible campaign. ENISA's threat landscape reporting attributes a measurable share of 2024 social-engineering incidents to generative tooling, and phishing-derived initial access remains above 30% of observed intrusions. Defenders respond by replacing static rules with behavioral models that score sequences rather than artifacts. Vendors that ship retrained models on a weekly cadence command higher renewal rates than annual-signature competitors [9].

Cloud and Multi-Cloud Migration Dissolves the Perimeter

Global enterprise cloud infrastructure spending exceeded USD 300 billion in 2024, and the share of workloads spanning two or more providers passed 80% among large firms. Each additional provider multiplies identity boundaries, API surfaces, and misconfiguration risk. Posture management and workload telemetry pipelines therefore attach to migration budgets rather than security budgets, an accounting shift that expands the addressable pool. Consumption-based pricing further lowers the threshold for mid-market adoption [10].

Talent Shortage Shifts Spend Toward Managed Delivery

Supply-Chain Exposure Widens Assessment Scope

Third-party compromise accounted for a rising share of confirmed breaches, with Verizon's 2025 analysis roughly doubling the prior year's proportion attributable to partners and suppliers. NIS2 explicitly extends duty of care to supplier relationships, and the U.S. Executive Order on software security requires attestation for federal vendors. Buyers now procure continuous vendor monitoring alongside internal detection, adding an estimated 10–15% to typical program scope and lengthening but enlarging deals [12].

Cyber Insurance Underwriting Codifies Minimum Controls

Insurers have moved from questionnaires to technical attestation, and carriers routinely decline or surcharge applicants lacking endpoint detection, multifactor authentication, and immutable backup. Global cyber premium volume approached USD 16 billion in 2024, and renewal pricing differentials of 15–25% between compliant and non-compliant risks create a direct financial return on control deployment. Insurance requirements effectively function as private regulation across mid-market segments that no statute reaches [13].

Restraints Impact Analysis

Restraint ~% Drag on CAGR Geographic Relevance Impact Timeline
Tool sprawl and integration fatigue 1.3 North America, Europe Short-term (≤2 yr)
Alert volume and analyst burnout 1.0 Global Short-term (≤2 yr)
Budget scrutiny and ROI proof burden 0.9 Global Medium-term (2–4 yr)
Data sovereignty limits on cloud analytics. 0.7 Europe, Asia-Pacific Medium-term (2–4 yr)
Legacy and operational technology incompatibility 0.6 Global Long-term (≥4 yr)


Tool Sprawl Slows New Purchases

Large enterprises average 45 to 76 discrete security tools, and consolidation initiatives now precede net-new purchases in most refresh cycles. Procurement teams increasingly require displacement of two existing licenses before approving one addition. This compresses vendor count faster than it compresses spend, but it stretches sales cycles by roughly 30% and favors incumbents with broad platforms over specialist entrants [14].

Alert Volume Erodes Realized Value

Security operations teams triage thousands of daily alerts with false-positive rates that industry surveys place between 20% and 45%. When realized detection value falls short of the promise, renewal conversations turn adversarial. Buyers now negotiate tuning commitments and measurable dwell-time reductions into contracts, which shifts risk to vendors and delays revenue recognition on multi-year agreements [15].

ROI Proof Burden Delays Approvals

Security spending growth moderated from mid-teens to high single digits in several 2024 CIO surveys as finance functions applied capital discipline. Detection platforms struggle to demonstrate return because success is an absence of loss. Programs without a quantified breach-cost baseline — the global average sits near USD 4.4 million per incident — routinely stall one to two budget cycles before approval [16].

Sovereignty Rules Constrain Cloud Analytics

GDPR transfer restrictions, India's Digital Personal Data Protection Act, and China's data localization framework limit where telemetry can be processed. Vendors must operate in-region analytics estates, raising infrastructure costs and delaying feature parity in smaller markets by 12 to 18 months. Regulated buyers consequently retain on-premise collection layers, which explains the durability of on-premise revenue despite faster cloud growth [17].

Legacy and Operational Technology Resist Instrumentation

Industrial control systems with 15- to 25-year service lives often cannot host modern agents, and vendor warranties frequently void on unapproved software installation. Passive network monitoring substitutes but delivers narrower visibility. Retrofitting a mid-sized plant typically costs USD 500,000 to USD 2 million and requires scheduled outages, pushing OT coverage into multi-year capital plans rather than annual security budgets [18].

Advanced Persistent Threat (APT) Protection Market Opportunities

Outcome-Based Contracting Around Dwell Time

Vendors that guarantee measurable dwell-time reduction convert a technical claim into a commercial instrument. Contracts tying 15–20% of fees to mean-time-to-detect thresholds are gaining traction in financial services, where DORA already requires evidence of resilience testing. The model addresses the ROI objection directly and raises switching costs once baselines are jointly established. Providers with mature telemetry can price this risk; specialists without historical baselines cannot, which concentrates the opportunity among platform incumbents.

Mid-Market Penetration in Emerging Economies

India, Indonesia, Vietnam, Brazil, and Saudi Arabia together host several million firms above the 250-employee threshold that regulators increasingly treat as in-scope. India's CERT-In six-hour incident reporting rule applies regardless of company size, creating an obligation without capability. SaaS-delivered detection priced between USD 4 and USD 12 per endpoint monthly meets that gap. Channel partners rather than direct sales will capture most of this volume, and vendors with localized support in-language will outperform.

Telemetry Monetization and Intelligence Subscriptions

Aggregated detection telemetry supports a second revenue line: curated intelligence feeds sold back to customers, insurers, and government partners. Feeds priced from USD 50,000 to USD 400,000 annually carry gross margins above 80% because collection cost is already sunk. Insurers in particular will pay for anonymized incident frequency data to price policies more precisely. Privacy constraints require careful anonymization design, but the model turns installed base scale into structural advantage.

Operational Technology and Critical Infrastructure Coverage

Fewer than half of industrial operators report continuous monitoring across their OT estates. Passive detection appliances that require no agent installation sidestep the warranty problem and open a segment where competition remains thin. The U.S. Bipartisan Infrastructure Law allocated USD 1 billion in state and local cybersecurity grants through 2025, much of it directed at utilities and transit. Vendors with protocol-level fluency in Modbus, DNP3, and IEC 61850 face limited rivalry.

Post-Quantum Readiness as an Adjacent Attachment

NIST finalized its first post-quantum standards in August 2024, and U.S. federal agencies face migration timelines extending to 2035. Harvest-now-decrypt-later collection makes this an active detection concern, not a future one. Vendors can attach cryptographic inventory and anomalous-collection detection to existing platforms at incremental cost, creating a new line item inside approved budgets.

Advanced Persistent Threat (APT) Protection Market Future Outlook

Autonomous Response Becomes the Default Posture

Detection is becoming a solved commodity; response speed is not. By 2030, most enterprise deployments will execute containment actions — host isolation, credential revocation, session termination — without analyst approval for defined confidence thresholds. The constraint is not model quality but organizational trust: a false isolation during trading hours costs more than a missed alert. Vendors will differentiate on graduated autonomy, allowing customers to expand machine authority as confidence accrues. Expect autonomous action coverage to move from roughly 15% of incidents today toward half by the early 2030s.


Identity Displaces the Network as the Control Plane

Credential abuse rather than malware now initiates the majority of significant intrusions, and that ratio continues shifting. Detection architectures built around network chokepoints lose relevance as traffic encrypts and workloads distribute across providers. Identity providers, privilege management vendors, and detection platforms are converging on shared session-risk models. By 2032, identity telemetry will likely constitute the largest single input to enterprise detection pipelines, restructuring both product architecture and vendor partnership maps.

Post-Quantum Migration Creates a Decade-Long Workstream

NIST's 2024 standards started a clock. U.S. federal guidance targets substantial migration by 2035, and the Office of Management and Budget has estimated federal transition costs at roughly USD 7.1 billion through that horizon. Detection vendors gain adjacent scope: cryptographic asset inventory, identification of vulnerable protocol usage, and monitoring for bulk encrypted-data exfiltration consistent with harvest-now-decrypt-later collection. This attaches new budget to existing platforms without requiring a separate procurement, which is why it appears as a growth contributor late in the forecast.

Advanced Persistent Threat (APT) Protection Market Segmentation

By Offering

Segmentation of the Advanced Persistent Threat Protection Market by offering separates delivered technology from the professional and managed work that makes it operational.

Segment Metric Primary Demand Driver
Solutions 11.72% CAGR (2026–2035) Platform consolidation and behavioral analytics
Services 51.2% share (2025) Deployment complexity and talent scarcity


Services hold the larger share with 51.2% (2025) because deploying detection is not a software installation. Integration engagements map platforms onto existing stacks, tune baselines against normal traffic, and align rules to MITRE ATT&CK coverage without generating unusable alert volume. Solutions grow faster as consolidated platforms displace point products and as behavioral models replace signature libraries. The two move together: every solutions renewal carries attached tuning and support work, which is why the services share erodes only gradually across the forecast.

By Solution Type

Solution-type distribution within the Advanced Persistent Threat Protection Market shows endpoint agents retaining primacy while intelligence platforms scale from a smaller base.

Segment Metric Primary Demand Driver
Endpoint Protection 23.8% share (2025) Remote work and device sprawl
SIEM USD 1.09 Billion (2025) Log retention mandates
Threat Intelligence Platforms 13.2% CAGR (2026–2035) Curated feed demand and alert enrichment
Intrusion Prevention Systems 12.4% share (2025) Perimeter and segment enforcement
Sandboxing USD 0.42 Billion (2025) Malware detonation and triage speed
Cloud Security Posture Management 12.9% CAGR (2026–2035) Multi-cloud misconfiguration drift
Security Orchestration and Automation 10.8% share (2025) Analyst capacity constraints
Forensic Analysis USD 0.31 Billion (2025) Regulatory investigation requirements


Endpoint protection leads with 23.8% share (2025) because the endpoint remains where intrusions become visible, and modern agents fold behavioral analysis, isolation, and forensic collection into one deployment. Threat intelligence platforms grow fastest at a 13.2% CAGR (2026–2035) as buyers move from raw feeds to curated, ATT&CK-mapped context that materially improves triage precision. SIEM revenue persists on the strength of retention mandates even as architectures shift toward cloud data fabrics, while posture management rides directly on multi-cloud expansion.

By Service Type

Service composition in the Advanced Persistent Threat Protection Market is shifting from project work toward continuous outcome delivery.

Segment Metric Primary Demand Driver
Integration and Deployment 34.9% share (2025) Stack complexity and tuning requirements
Managed Security Services 13.8% CAGR (2026–2035) Analyst shortage and 24/7 coverage need
Support and Maintenance USD 0.67 Billion (2025) Model retraining and patch cadence
Consulting 15.3% share (2025) Compliance framework alignment
Training and Education 11.1% CAGR (2026–2035) Human-factor risk reduction


Integration and deployment still commands a 34.9% share (2025), making it the largest share because every meaningful implementation requires calibration against a specific environment. Managed security services grow fastest, converting fixed analyst headcount into a variable subscription that mid-sized organizations can actually staff. Consulting demand tracks compliance cycles rather than technology cycles, spiking around NIS2 and DORA deadlines. Training has shifted from annual workshops toward continuous micro-learning tied to observed employee risk behavior.

By Deployment Mode

Deployment preference in the Advanced Persistent Threat Protection Market balances sovereignty constraints against elasticity and cost.

Segment Metric Primary Demand Driver
On-Premise USD 3.20 Billion (2025) Data sovereignty and latency requirements
Cloud 13.35% CAGR (2026–2035) Elastic analytics and consumption pricing
Hybrid 15.8% share (2025) Regulated workload separation


On-premise retains the revenue lead with USD 3.20 billion (2025)because regulated industries and government buyers cannot export telemetry across jurisdictions. Cloud grows fastest at a 13.35% CAGR (2026–2035) as analytics workloads outstrip what local hardware can economically process, and as consumption pricing removes the capital hurdle for mid-market entry. Hybrid is less a category than a destination: most large deployments now keep collection local while sending enriched, anonymized events to cloud analytics, and vendors design for that split by default.

By Enterprise Size

Enterprise-size segmentation of the Advanced Persistent Threat Protection Market reflects budget depth on one side and regulatory reach on the other.

Segment Metric Primary Demand Driver
SMEs 11.28% CAGR (2026–2035) SaaS delivery and insurance requirements
Large Enterprises 62.8% share (2025) Compliance exposure and adversary targeting


Large enterprises dominate revenue with 62.8% share (2025) because they carry the compliance obligations, hold the assets adversaries pursue, and can fund platform consolidation programs that collapse multiple agents into one console. SMEs grow faster at an 11.28% CAGR (2026–2035 from a smaller base as regulation stops exempting them — India's CERT-In rules and cyber insurance underwriting apply irrespective of headcount. Auto-configuring baselines and AI-guided investigation make deployment feasible without dedicated staff, which is the binding constraint in that segment.

By Vertical

Vertical distribution in the Advanced Persistent Threat Protection Market follows regulatory intensity and the value of the data at stake.

Segment Metric Primary Demand Driver
BFSI 27.1% share (2025) DORA and financial supervisory mandates
Government and Defense USD 1.02 Billion (2025) National security and CDM programs
Healthcare 11.4% share (2025) Patient data protection and device security
IT and Telecom 13.6% share (2025) Infrastructure operator obligations
Manufacturing 10.9% CAGR (2026–2035) OT convergence and supply-chain clauses
Retail and E-Commerce 11.72% CAGR (2026–2035) Payment data and fraud exposure
Energy and Utilities USD 0.51 Billion (2025) Critical infrastructure targeting
Others 6.2% share (2025) Sector-specific digitization


BFSI leads with 27.1% share (2025)on regulatory intensity: DORA, supervisory stress testing, and direct financial motive make detection non-discretionary. Retail and e-commerce grow fastest at a 11.72% CAGR (2026–2035) as payment-data breaches and fraud losses justify investment that thin margins previously suppressed. Manufacturing accelerates on OT convergence and on security clauses inherited from customers rather than regulators. Government and defense spending remains large but procurement-cycle bound, delivering steady rather than rapid expansion.

Regional Market Share Analysis

Region Metric Primary Investment Themes
North America 34.1% share (2025) Federal mandates, financial services, OT retrofits
Europe USD 1.62 Billion (2025) NIS2 and DORA compliance, sovereign cloud
Asia-Pacific 11.36% CAGR (2026–2035) Manufacturing digitization, national CERT rules
South America USD 0.34 Billion (2025) Banking modernization, ransomware response
Middle East & Africa 10.94% CAGR (2026–2035) Sovereign programs, energy infrastructure
Total USD 5.71 Billion (2025)

Regional distribution in the Advanced Persistent Threat Protection Market reflects regulatory density, financial-sector concentration, and cloud maturity. North America leads on installed base and federal procurement scale, while Asia-Pacific compounds fastest from a smaller base as national frameworks mature.


North America

Country Share of Region Key Driver
US 86.4% Federal CDM funding and SEC disclosure rule
Canada 9.1% Bill C-26 critical cyber systems protection
Mexico 4.5% Nearshoring manufacturing security requirements


Federal procurement sets the tone across North America. CISA's Continuous Diagnostics and Mitigation program has obligated over USD 6 billion since 2013, and the FY2025 civilian cybersecurity request of roughly USD 13 billion sustains multi-year task orders that commercial buyers use as reference architectures. The SEC's incident disclosure rule, effective December 2023, converted detection speed into a securities-law exposure for every listed issuer. Canada's Bill C-26 extends comparable obligations to telecommunications, banking, energy, and transportation operators. Mexico's growth traces to nearshoring: manufacturers serving U.S. supply chains inherit customer security clauses that domestic regulation would not otherwise impose.

Europe

Country Share of Region Key Driver
Germany 23.4% BSI Act implementation and industrial OT exposure
UK 20.1% Cyber Security and Resilience Bill
France 15.2% ANSSI certification requirements
Italy 9.6% ACN national perimeter framework
Spain 7.8% Public sector digitization funding
Nordic Countries 8.3% Maritime and energy infrastructure focus
Russia 5.1% Domestic vendor substitution
Rest of Europe 10.5% Cross-border NIS2 transposition


NIS2 dominates European demand. The directive's October 2024 transposition deadline slipped in several member states. However, national laws in Germany, Italy, and the Nordics have since imposed management liability that makes security spending a personal exposure for directors. DORA layered financial-sector obligations on top from January 2025, requiring threat-led penetration testing modeled on the TIBER-EU framework. Data residency complicates vendor architecture: German and French buyers frequently demand in-country processing, which favors suppliers operating sovereign cloud regions. The UK, outside NIS2, is advancing its own Cyber Security and Resilience Bill with broadly parallel scope.

Asia-Pacific

Country Share of Region Key Driver
China 30.6% Multi-Level Protection Scheme 2.0 compliance
India 18.4% CERT-In six-hour reporting directive
Japan 17.9% Active Cyber Defense legislation
South Korea 11.2% Financial sector security regulation
ASEAN 13.7% Cross-border digital economy frameworks
Rest of Asia-Pacific 8.2% Government digitization programs


Asia-Pacific compounds fastest because obligation is arriving ahead of capability. India's CERT-In directive requires incident reporting within six hours and mandates 180-day log retention within national borders, a standard that forces tooling upgrades at firms with no prior security operations function. Japan passed Active Cyber Defense legislation in 2025 permitting pre-emptive measures against hostile infrastructure, expanding government demand. China's Multi-Level Protection Scheme 2.0 grades systems into five tiers with escalating technical requirements, though domestic vendors capture most of that spend. ASEAN members are converging on a common incident-reporting baseline that will pull mid-market adoption forward.

South America

Country Share of Region Key Driver
Brazil 58.3% LGPD enforcement and banking sector mandates
Argentina 16.7% Financial services modernization
Rest of South America 25.0% Public sector ransomware response


Brazil anchors the region. The Central Bank's cybersecurity resolution requires incident response plans and cloud contracting controls from every regulated financial institution, and LGPD enforcement has produced escalating administrative penalties since 2023. Ransomware against public bodies — including high-profile disruptions to Chilean and Colombian government systems — moved cybersecurity from an IT line item to a cabinet-level concern across several administrations. Procurement remains price-sensitive and heavily channel-mediated, so vendors compete on local partner depth and Portuguese or Spanish-language support rather than feature breadth. Managed delivery dominates because in-house analyst hiring is difficult at prevailing salary bands.

Middle East & Africa

Country Share of Region Key Driver
Saudi Arabia 34.2% NCA Essential Cybersecurity Controls
UAE 27.6% Dubai Cyber Security Strategy and DIFC rules
South Africa 14.1% POPIA compliance and financial services
Egypt 8.7% Government digitization program
Rest of MEA 15.4% Energy and telecom infrastructure


Gulf state programs drive regional spending. Saudi Arabia's National Cybersecurity Authority mandates Essential Cybersecurity Controls across government and critical sectors, with Vision 2030 allocating substantial capital to digital infrastructure that carries security requirements by design. The UAE combines federal frameworks with emirate-level rules and DIFC data protection obligations for financial firms. Energy operators across the region face documented targeting of process control networks, making OT-aware detection a procurement priority rather than an upgrade. South Africa's demand concentrates in banking and telecommunications, where POPIA penalties and cross-border operations impose obligations that broader domestic regulation does not.

Advanced Persistent Threat Protection Market By Region, 2025-2035

Competitive Benchmarking

The Advanced Persistent Threat Protection Market shows medium concentration. The top five vendors hold an estimated 33–38% of global revenue, and the Herfindahl-Hirschman Index sits near 620 — below the 1,500 unconcentrated threshold, indicating genuine competitive rivalry rather than oligopoly. Structure is barbelled: platform incumbents bundle detection into broad suites and compete on consolidation economics, while specialist vendors win on detection efficacy in specific environments. Acquisition activity has thinned the middle, and the practical differentiator increasingly is telemetry breadth rather than algorithm quality, since detection models improve with data volume.

Company Est. Revenue Share Range Key Offerings for Advanced Persistent Threat Protection Market Strategic Positioning
Palo Alto Networks ~9–12% Cortex XDR, XSIAM, Unit 42 response services Platform consolidation leader; aggressive suite bundling
CrowdStrike ~8–11% Falcon endpoint, Falcon Complete managed detection Cloud-native single agent; strong managed attach
Microsoft ~7–10% Defender XDR, Sentinel, Entra identity protection Bundled licensing advantage via enterprise agreements
Cisco ~5–8% Secure Endpoint, XDR, Talos intelligence Network telemetry depth; large installed base
Trellix ~4–6% Endpoint security, network detection, sandboxing Post-merger consolidation of enterprise portfolio
Fortinet ~4–6% FortiEDR, FortiSandbox, FortiGuard services Price-performance in mid-market and distributed sites
Trend Micro ~3–5% Vision One XDR, cloud workload protection Strong Asia-Pacific and Japanese enterprise presence
Broadcom (Symantec) ~3–5% Endpoint security complete, threat intelligence Large-account focus; regulated industry retention
Check Point ~3–4% Infinity XDR, SandBlast threat emulation Prevention-first architecture; European strength
Sophos ~2–4% Intercept X, managed detection and response Mid-market and channel-led delivery
SentinelOne ~2–4% Singularity platform, autonomous response Autonomous action emphasis; rapid enterprise gains
IBM ~2–4% QRadar Suite, X-Force incident response Services-led; consulting and integration depth


Recent News & Developments

  • European Commission (October 2024): The NIS2 transposition deadline passed, obligating member states to apply expanded incident-reporting and supply-chain security rules to an estimated 160,000 entities, triggering measurable procurement acceleration across regulated European sectors. [4]
  • NIST (August 2024): Finalized the first three post-quantum cryptography standards, initiating enterprise cryptographic inventory projects that detection vendors are now attaching to existing platform contracts. [7]
  • European Supervisory Authorities (January 2025): DORA became applicable to EU financial entities, mandating threat-led penetration testing and ICT third-party risk registers, and lifting BFSI detection spend across the bloc. [5]


  • CISA (March 2024): Issued advisories documenting sustained pre-positioning by state-linked actors inside U.S. critical infrastructure operational technology networks, shifting utility procurement toward continuous hunting capability. [8]
  • Government of Japan (May 2025): Enacted Active Cyber Defense legislation permitting pre-emptive measures against hostile infrastructure, expanding public-sector detection and attribution requirements. [20]
  • CrowdStrike (September 2024): Expanded managed detection coverage with new response service-level commitments, formalizing outcome-based contracting terms that competitors have since matched. [21]
  • SEC (December 2023): Cybersecurity incident disclosure rules took effect for listed issuers, requiring materiality determination and four-business-day reporting, which elevated detection speed to a board-level financial exposure. [3]

Advanced Persistent Threat (APT) Protection Market Report Scope

Parameter Detail
Market Scope Global market for solutions and services that detect, analyze, contain, and remediate multi-stage targeted intrusions across endpoint, network, cloud, and identity layers
Study Period 2021–2035 (Historical: 2021–2024; Base Year: 2025; Forecast: 2026–2035)
CAGR 11.02% (2026–2035)
Market Size Checkpoints USD 5.71 Billion (2025); USD 6.34 Billion (2026); USD 9.63 Billion (2030); USD 16.42 Billion (2035)
Fastest Growing Segments Managed Security Services (13.8% CAGR); Cloud deployment (13.35% CAGR); Threat Intelligence Platforms (13.2% CAGR)
Companies Profiled Palo Alto Networks, CrowdStrike, Microsoft, Cisco, Trellix, Fortinet, Trend Micro, Broadcom (Symantec), Check Point, Sophos, SentinelOne, IBM
Valuation Currency USD Billion, constant 2025 dollars

FAQs

How should buyers structure a proof-of-concept evaluation in the Advanced Persistent Threat Protection Market?
Run the evaluation against live production telemetry for at least 30 days, not vendor-supplied test data. Measure false-positive rate and analyst hours consumed, not detection counts. [15]
What contract terms most affect total cost of ownership?
Data ingestion pricing dominates. Per-gigabyte SIEM models can double costs as logging expands, so negotiate committed-volume tiers and retention flexibility upfront. [16]
Does cyber insurance reduce the need to invest in the Advanced Persistent Threat Protection Market?
No. Carriers now require endpoint detection, multifactor authentication, and immutable backup as underwriting preconditions, and non-compliant applicants face surcharges of 15–25% or outright declination. [13]
How do buyers evaluate detection coverage objectively?
Map vendor claims against MITRE ATT&CK techniques relevant to your sector, then request independent evaluation results. Coverage breadth matters less than depth on techniques your adversaries actually use. [8]
What integration problems most often derail deployments in the Advanced Persistent Threat Protection Market?
Legacy identity directories and unsupported operating system versions cause most delays. Audit agent compatibility across the full estate before signing, since exceptions become permanent blind spots. [18]
Should mid-sized firms build a security operations function or outsource it?
Outsource below roughly 2,000 employees. A 24/7 in-house rotation requires eight to ten analysts, which exceeds what most mid-market salary bands and retention rates can sustain. [11]
How does post-quantum migration affect current detection purchases?
Ask vendors for cryptographic inventory capability now. Harvest-now-decrypt-later collection is an active exfiltration pattern, and platforms without crypto-agility roadmaps will need replacement before 2035. [7]
Author
Author
Author Profile
Aarti Dhapte LinkedIn AVP - Research
A consulting professional focused on helping businesses navigate complex markets through structured research and strategic insights. I partner with clients to solve high-impact business problems across market entry strategy, competitive intelligence, and opportunity assessment. Over the course of my experience, I have led and contributed to 100+ market research and consulting engagements, delivering insights across multiple industries and geographies, and supporting strategic decisions linked to $500M+ market opportunities. My core expertise lies in building robust market sizing, forecasting, and commercial models (top-down and bottom-up), alongside deep-dive competitive and industry analysis. I have played a key role in shaping go-to-market strategies, investment cases, and growth roadmaps, enabling clients to make confident, data-backed decisions in dynamic markets.

Research Approach


Secondary Research

The secondary research process involved comprehensive analysis of cybersecurity frameworks, threat intelligence databases, regulatory compliance repositories, and authoritative technology publications. Key sources included the US Cybersecurity and Infrastructure Security Agency (CISA), National Institute of Standards and Technology (NIST), European Union Agency for Cybersecurity (ENISA), UK National Cyber Security Centre (NCSC), MITRE Corporation (ATT&CK Framework), Common Vulnerabilities and Exposures (CVE/NVD) database, Verizon Data Breach Investigations Report (DBIR), IBM X-Force Threat Intelligence, INTERPOL Cyber Fusion Centre, FIRST (Forum of Incident Response and Security Teams), Cloud Security Alliance (CSA), (ISC)² Global Information Security Workforce Study, SANS Institute Reading Room, and national CERTs (Computer Emergency Response Teams) from key markets. These sources were used to collect threat landscape statistics, regulatory compliance requirements (GDPR, NIS2 Directive, HIPAA, PCI-DSS, SOX), incident response data, patent filings for detection algorithms, and competitive intelligence for AI/ML-based threat detection technologies.


Primary Research

Qualitative and quantitative insights were obtained by interviewing supply-side and demand-side stakeholders during the primary research process. CEOs, Chief Technology Officers (CTOs), Chief Information Security Officers (CISOs), Vice Presidents of Product Development, heads of threat intelligence/research, and commercial directors from APT protection platform vendors, cybersecurity OEMs, and managed security service providers (MSSPs) comprised supply-side sources. BFSI institutions, healthcare systems, government agencies, telecommunications operators, and critical infrastructure operators comprised demand-side sources, which included CISOs, Chief Information Officers (CIOs), IT Security Directors, Security Operations Center (SOC) Managers, network security architects, and procurement leads. Primary research verified market segmentation across solution types, confirmed product roadmap timelines for zero-day detection capabilities, and collected insights on enterprise adoption patterns, pricing strategies for subscription-based models, and procurement cycles for security infrastructure.

Primary Respondent Breakdown:

• By Designation: C-level Primaries (40%), Director Level (25%), Manager/Specialist Level (35%)

• By Region: North America (40%), Europe (25%), Asia-Pacific (28%), Rest of World (7%)


Market Size Estimation

Global market valuation was derived through software revenue mapping and enterprise deployment analysis. The methodology included:

• Identification of 50+ key cybersecurity vendors across North America, Europe, Asia-Pacific, Latin America, and Middle East & Africa

• Product mapping across network security, endpoint detection and response (EDR), email security, cloud workload protection platforms (CWPP), deception technology, and threat intelligence platforms

• Analysis of reported annual recurring revenue (ARR) and license revenue specific to APT protection portfolios, including both on-premises perpetual licenses and cloud-based SaaS subscriptions

• Coverage of vendors representing 75-80% of global market share in 2024

• Extrapolation using bottom-up (enterprise seat count × average selling price by deployment mode) and top-down (vendor revenue validation adjusted for MSSP margins) approaches to derive segment-specific valuations for solution types, service categories, and vertical industry adoption rates

Download Free Sample

Kindly complete the form below to receive a free sample of this Report

Download PDF ×

We do not share your information with anyone. However, we may send you emails based on your report interest from time to time. You may contact us at any time to opt-out.